Showing posts with label attachments. Show all posts

Tuesday, December 12, 2017

Ho-Ho-Holiday Spams and Scams

   It's that time of year again folks.  And whatever holiday you may, or may not, celebrate... there's something we're all likely to see.  It's not presents, though maybe there are some for you.  It's not snow, though we're already seeing that here in the upper midwest US.

   It's malware and holiday scams!

   Unfortunately, it happens every year.  Sometimes it's malicious attachments.  Sometimes it's links to malware to download or phishing sites with forms ready to collect your personal and financial information.

   Here is my 2017 edition of my Top 10 Tips To Avoid Holiday Spams and Scams...

Tuesday, September 6, 2016

Call Me

  I recently received some awesome news via email.  And it was totally unexpected.  Check it out:


   Now I can retire in style!  :-)

   Needless to say, this is a phishing email.  We've talked about phishing many times in the past.  And we keep talking about it.

   So why does phishing still work?  There are two primary reasons:
  1. No cost/low barrier to entry.  It is effectively free to send out potentially millions of phishing or spam emails.  Attackers can easily relay email through open mail relay servers, but there are other ways to send spam and phishing emails.  Open mail relays are systems that send email but don't require any kind of identification.  Here's some more technical info on open relays.
  2. Exploiting the human factor.  People are busy and we all receive too much email.  It's not always easy to take the time to figure out if an email is OK or not.  Attackers leverage this by sending plausible-looking email, though there are plenty of poorly-created messages as well (like the one above that I received).
   As I mentioned in a previous column, rather than looking examining an email for evidence of phishing, we can approach all email as if it's hostile and then look for indications that it's OK.

   If you'd like to have some fun... try these spot the phishing online quizzes!

   I won't be contacting the "friend" to sent me the above email.  And I did not win.

   Have you seen any interesting phishing emails you'd like to share?

Tuesday, July 12, 2016

Brexit Protection - click here

   Brexit Protection... or should we call it Brexitection? :-)

   How does Brexit affect your finances?  Do you care?  Plenty of people do.

   And that creates an opportunity for scammers.

   Any time there are major news events, particularly disasters or anything economic, people get worried. and the scammers are right there to play on those fears.

   According to the Telegraph, they have seen emails with subjects such as "Brexit causes historic market drop". These emails have links that supposedly connect to pages with information on how to protect your investments.  Of course, they actually download malware to the victims computer.

   This is a common problem... common because it works.

   We've covered this topic before... and the advice remains the same.  In fact, here are my top 10 email scam tips from a 2013 post!  These are just as relevant today as then.  And they will be relevant years from now:

Tuesday, June 28, 2016

We're Going About It All Wrong

   Phishing, scam, spam and malicious emails are an ongoing problem.  A recent study found that rates of these malicious emails are worst in months that have an "a", "u" or "r" in the name, with highest delivery volumes on days ending in a "y".

   Seriously though, while the worldwide spam volume seems to be trending down since a peak over 70% in 2014, rates were trending up in the first quarter of 2016 and the percentage of email that is spam or malicious is well over 50%.

   Email, along with malicious files on websites (whose links are usually delivered through email!), continue to be the top malware vectors.

   In fact, attackers don't even need to use their best, or most complex, attack methods.  It's far more cost-effective to send out random or targeted email, or to place random malicious files on websites and email out the links.  Remember, most cybercrime is economically motivated.  It's a business and the goal is ROI (return on investment).  And business is good.

   It's a big problem because we are fundamentally trusting beings.  I've always believed that people want to do the right thing.  When it comes to people, we should assume positive intent.

   However, email is not a person.

Tuesday, February 23, 2016

Hospital Held Hostage, FBiOS and CEO Phishing

   I usually don't do "news of the week" commentary posts, but too much has happened this past week and we need to discuss it!

Hospital Held Hostage.

   I'm sure by now you've seen some info on what happened at Hollywood Presbyterian Medical Center in California.  Just in case you were on a desert island... on Feb. 5 HPMC experienced a cryptoware attack.  We've talked about those before... it's malicious software that encrypts files so that only the attacker can read them... the people who need to can't.  The story broke about 10 days later.

   Cryptoware becomes ransomware when the attackers offer to fix the problem - decrypt the files - for a "small consulting fee", usually not small and paid in bitcoin, an untraceable online currency.

   The situation itself is, unfortunately, not unique.  These kinds of attacks have been happening everywhere for years.  But there are two things that happened in this case that are unique.  First, the cryptoware completely shut down all the computerized systems in the hospital.  That means no electronic medical records, radiology, anesthesiology... just about any -ology and most hospital functions are computerized.  The hospital reverted to paper and had to turn away surgery patients or those needing more complex diagnosis, tests or procedures.  

   Second, the hospital paid the ransom.  This is the first publicized case of both a hospital shut down in this way and paying the ransom to restore their files.

   Most hospitals have procedures, called "down time procedures" for operating without some computerized resources.  And there is an incident handling process called HICS - Hospital Incident Command System - based on US FEMA (Federal Emergency Management Agency) NIMS (National Incident Management System).  But there are still medical procedures that can't be done with out access to the electronic data or computer-controlled systems.

   This attack is not OK.  Stealing people's data is bad enough.  But this affects lives.

FAQ:
   Can this happen here (wherever "here" is)?  It can, it has, it does and it will.  All industries and even home systems have been hit.  It's not "if", but "when".

   Can't we prevent it?  Yes!

   Wait.  What?  There's more to that story.  An attack like this can be prevented, but systems would have to be locked down so tight that they might not be usable.  And that's not a solution.  But there are some proactive things that can be done:
  • Don't click!  Most of these kinds of attacks start with the click of a link on a website or in an email, or opening an email attachment.  We've discussed this many times before... if you're not expecting it, if it doesn't look right, if it's not consistent... don't click!
  • Endpoint controls.  These are controls on your desktop or laptop computer including old-school anti-virus, application whitelisting, and execution controls; operational procedures like having a standard workstation configuration and regular patching.
  • Network/System controls.  Like monitoring and keeping all applications up to date with the latest versions and patches, and reliable and tested offline backups.
  • Internet controls.  Like web site filtering and email controls.
   So why did they pay?  Isn't that bad?  In some cases, if the cryptoware infection gets so bad that the organization cannot recover, there may be no other choice then to pay.  And even that's no guarantee that the attackers will or can give you the key to decrypt the files.  In some attacks, if the victim doesn't pay in time, the key is deleted and the files could be unrecoverable.  It's obviously better not to pay (or not to have to pay!), but the organization might not have a choice.

   CSI:Cyber did an episode on a hospital malware attack in Nov. 2015.  I wrote about that here.

   Just a quick commentary on the other two issues.

CEO Phishing.

   Or perhaps more correctly... phishing from your CEO!  In this phishing attack variant, an email comes from "the CEO" (or other highly placed official) demanding some kind of immediate action, typically involving wiring money.  All too often, the recipient does what they're told and sends the funds.

   Recent issues in the US and in France have kept this in the news.  Now Microsoft is getting in on the act, trying to make improvements to Outlook to help with this problem.

   As we've discussed in the past, if something on a web page or email doesn't look right, it probably isn't.  Don't click; Report it!  And even if you did click, report it!

FBiOS.

   After the San Bernadino, California terrorist shooting last December, Federal authorities captured one of the attacker's cell phone.  It is an Apple 5C.  Because of the way Apple encrypts its phones, law enforcement has been unable to view the contents of the phone.

   This week a federal judge ordered Apple to help unlock the phone.  The order is based upon the 1789 law called the All Writs Act.  Apple has chosen not to comply and that has led to plenty of discussion on both sides of the issue.  Apple says helping would set a bad precedent and weaken their phones' protections.  The FBI says it's Apple's duty to help with this criminal investigation.

   As is so often the case, there is no perfect answer.

   As Benjamin Franklin famously did not say, "Those who give up liberty for security deserve neither".  The reality for encryption is, if we make technology that law enforcement can crack, then anyone can crack it.  This is true because of the law no one can break - the law of mathematics!

   However, the Apple 5C uses an older encryption method than their newer phone.  So in this case, Apple could help without compromising everyone else's security and privacy.

   There's some great in-depth discussion of this issue on the TWIT podcast this week.

   Here are some good articles with more details.  We'll watch to see how this plays out.

Tuesday, January 12, 2016

New Year = Same Stuff

   It's a new year, but the same kind of online problems we've seen over the past few years are still here and are more prevalent than ever.

   Here's a great video about this issue by Media Pro:
Don't Let Malware Spoil the Fun from MediaPro on Vimeo. (I can't embed the video here, but do click on the link to view it.)

   The video reminds us that malware can, unfortunately, be found in many places including:
  • insecure websites
  • email attachments
  • browser add-ons
  • USB sticks
  • PDF files
   In additional to slowing down your system and causing it to not operate correctly, many kinds of malware try to grab your personal or work information.

   As we discussed here recently, your home computer defense toolkit should include:
  • anti-malware software
  • automatic updates
   But software tools are not enough.  You need to take action to protect your data and your computer:  Remember:
  1. You didn't win!...If it's too good to be true, it probably isn't true.
  2. Be careful with attachments, unknown programs, or files from USB sticks.
  3. Keep your software up to date.
   Let's do what we can to keep ourselves, our data (and our patients', customers' and clients' data) and our computers safe in 2016!

Monday, October 12, 2015

Keep Celebrating! - Mobile and Social

   We continue our celebration of US Cyber Security Awareness month!  This partnership between Homeland Security, NCSA (National Cyber Security Alliance) and the MS-ISAC (Multi-State Information Sharing and Analysis Center) is an opportunity to recognize the importance of information security.  It started in 2003 as a way to build awareness for online security and privacy and to encourage individuals, business and government.

   This is another of my weekly posts connected with the weekly themes put together by DHS.  This week the theme is staying protected while always connected.  That rhymes!

   We are always connected!  According to the Pew Research Center, in 2015 90% of american adults own a cell phone, 64% own a smart phone.  And one of the major uses for smart phones is... not calls but social media!  How do we stay safe online and on the move?

Monday, October 5, 2015

Celebrate! - A Culture of Security

   It's time again to celebrate that wonderful US event... Happy Cyber Security Awareness month!  This partnership between Homeland Security, NCSA (National Cyber Security Alliance) and the MS-ISAC (Multi-State Information Sharing and Analysis Center) is an opportunity to recognize the importance of information security.  It started in 2003 as a way to build awareness for online security and privacy and to encourage individuals, business and government.

   This month I'll be putting out weekly posts connected with the weekly themes put together by DHS.  This week the theme is creating a culture of security.

   The message is simple... in the workplace security is a team sport.  All organizations have customers, patients, systems and data to protect.  To accomplish this, security must be part of everyone's job.

Tuesday, August 18, 2015

Crypto Where?

   It's that scary moment...  You're getting some work done on your computer when you see a dreaded pop-up message:

   CryptoLocker, CryptoWall and other crypto-/ransom-ware has been in the news again (or still?).  This kind of malware attack was first identified in 2013.  Rather than trying to steal information, the malware encrypts your files.  But you don't have the key to decrypt.  The attacker offers, through a pop-up message, to "sell" you the "service" to unlock your files.  To make things worse, the attacker threatens to delete the keys after a set amount of time, typically 72 hours, which could prevent you from recovering the files.

   These ransom-ware viruses are usually sent to your computer as an email attachment.  The attachment can be an office file, pdf, zip file or other file.  The malware can also come from an infected web link.

   When your computer is infected, the virus operates quietly in the background, encrypting files.  You usually won't know there's a problem until the files are encrypted, and then you're in trouble.

   So if you are infected and encrypted... then what?  Well, there's bad news, good news, more bad news and some more potentially good news!

Tuesday, July 21, 2015

Must Click Immediately!

I received this email recently.  Looks legit and serious! :-)  I better open that attachment...


   While many people would recognize this as a problem, many others would click to see what info is in the attachment.

   We regularly read about advanced and targeted attacks.  While there is plenty of nasty malware out there, most attacks start with a click.  Make sure it's not yours!

   Here are some tips to help you recognize a phishing email.

Tuesday, February 24, 2015

It Wasn't Englebart's Fault! (part 1)

   Douglas Englebart was an engineer, inventor and pioneer of the early internet.  He died in 2013.  He was known for a number of key ideas and inventions.  In 1967, he invented a very useful computer device that is a key component in propagating malware and facilitating phishing attacks... the Mouse!

   Of course, Englebart didn't invent email, email attachments, phishing emails or malicious links.

   The media is always buzzing with information about the latest breach or computer break-in.  We hear about advanced attacks, nation-states and possibility of cyber-war.  Many of these major attacks start with a simple click (or many clicks).

   Two of the main ways that malware is distributed or information is stolen is via:

  • malicious attachments sent in an email, and;
  • phishing emails with malicious links.
   For either of these methods to work, the recipient of the email needs to click... with a mouse! (well, you could also use a track-pad or track-ball).  The attachment needs to be opened.  If it's a zip file, it needs to be unzip'd.  If it's a link, clicking the link might either download malware or lead to a form asking for personal information.  Any of these actions could cause major problems.

   Let's discuss two issues:
  • what do these viruses do?
  • why can't my organization stop these? (or why can't I stop them at home?)
   This is, unfortunately, pretty complex and we'll probably handle these in two separate posts.

Why Viruses?

   As I've discussed in the past, this is really an economics issue.  There's illicit money to be made and there are smart people out there coming up with new ways to attack and take over systems.

   A typical computer virus does 1 of 3 things (I'm using the term virus generically - a virus is actually just one of a number of different types of malware (malicious software)).  It can even do more than one of these:
  1. connect "home" and download more viruses;
        This is an optional step.  The real goals are items #2 and #3.
  2. take over a computer so it can be remotely controlled, or;
        An attacker can take over a bunch of computers and use them to attack other computers or sell that capability to others. The computers taken over are called robots or bots.  They can be used to spread spam and more malware; to send a lot of traffic at target computers so they won't work properly or at all (this is called Denial of Service or DoS), or; might use other attack methods.
  3. steal information (the techy word for this is exfiltration).
        The stolen personal or corporate information can be sold or used to steal money from existing or newly created accounts.
  4. (bonus item) threaten to do the above (blackmail).
        An attacker might threaten to crash computers if not paid.  One kind of malware called "ransomware" encrypts your files so that only the attacker can decrypt them and charges you a fee to get your access back.
What can we do?

   This is a complex issue and we'll talk about protection methods next time.  For now, the best advice is to take measures we've often discussed here:
  • use anti-malware software
  • use care when opening attachments
  • use care when clicking on links
  • know who sent you that email, message, tweet, social network message, etc.
   I discussed these and other steps you can take in a post last year.

Tuesday, October 7, 2014

Celebrate Cyber-Style!

   It's time again to celebrate that wonderful US event... Happy Cyber Security Awareness month!  This event started in 2003 as a way to build awareness for online security and privacy and to encourage individuals, business and government.

   Over the past couple of posts I've focused on Identity Fraud (here and here).  We'll pause on that topic until next time.

   Today I give you...  The Top 10 Ways to Celebrate Cyber Security Month 2014!
  1. Change your password
  2. Yes, I know... I said in the past that just changing your password is not the effective measure.  That's true but with the frequency with which online sites get compromised, it's not a bad idea.  Even better - use really long passwords.  Remember, when it comes to passwords... size matters!

  3. Use a password vault
  4. A password vault is a program that encrypts and holds all your passwords.  I explain these in detail, and list some good products, in this post.

  5. Look before you click
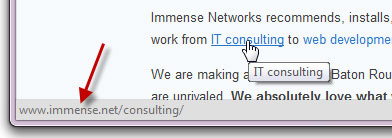
  6. With most links to can "mouse over" the link.  That means you just move your mouse so it's on the link, but don't click yet!  Your browser will display the address to which the link will lead.  This displays at the bottom of the browser.  The actual link in the display should make sense and be the location you're expecting.  If not then... don't click!

Tuesday, February 25, 2014

No, You Can't Have Local Admin!

   If you have responsibility for security and/or access management for an organization, then there is a "simple" request that you have received, and will always receive... Users request local admin access to systems.

   Most of you know what I mean.  I'm referring to the local administrator or root account on a system.  When a person has local admin, they can access any part of the system, change or disable settings (including deactivating anti-malware or other security software), and, perhaps most importantly, install and run any software.  This last item is probably the primary reason people request this level of access.

   We're talking about Minimum Necessary... the idea that everyone should have exactly the level of access needed to do their job, and no more.  In most, if not all, organizations, far more people have local admin than really need it.

   Security vendor Avecto recently released a new study showing that over 90% of the most serious vulnerabilities in Microsoft software products in 2013 could have been mitigated by simply removing administrator rights.  Put another way, this means that only your systems administrators were vulnerable to all of the most critical Microsoft software vulnerabilities!  And these are the people who have the most access on your systems!  Here are a two good articles on the subject and here is a link to the full report.

   Let's break this down...

Tuesday, November 19, 2013

It's That Time of Year - Holiday Spams and Scams

   It's that time of year again folks.  And whatever holiday you may, or may not, celebrate... there's something we're all likely to see.  It's not presents, though maybe there are some for you.  It's not snow, though we'll see that soon enough here in the upper midwest US.  It's malware and holiday scams!

   Unfortunately, it happens every year.  Sometimes it's malicious attachments.  Sometimes it's links to malware to download or phishing sites with forms ready to collect your personal and financial information.

   Here is my 2013 edition of my Top 10 Tips To Avoid Holiday Spams and Scams...